



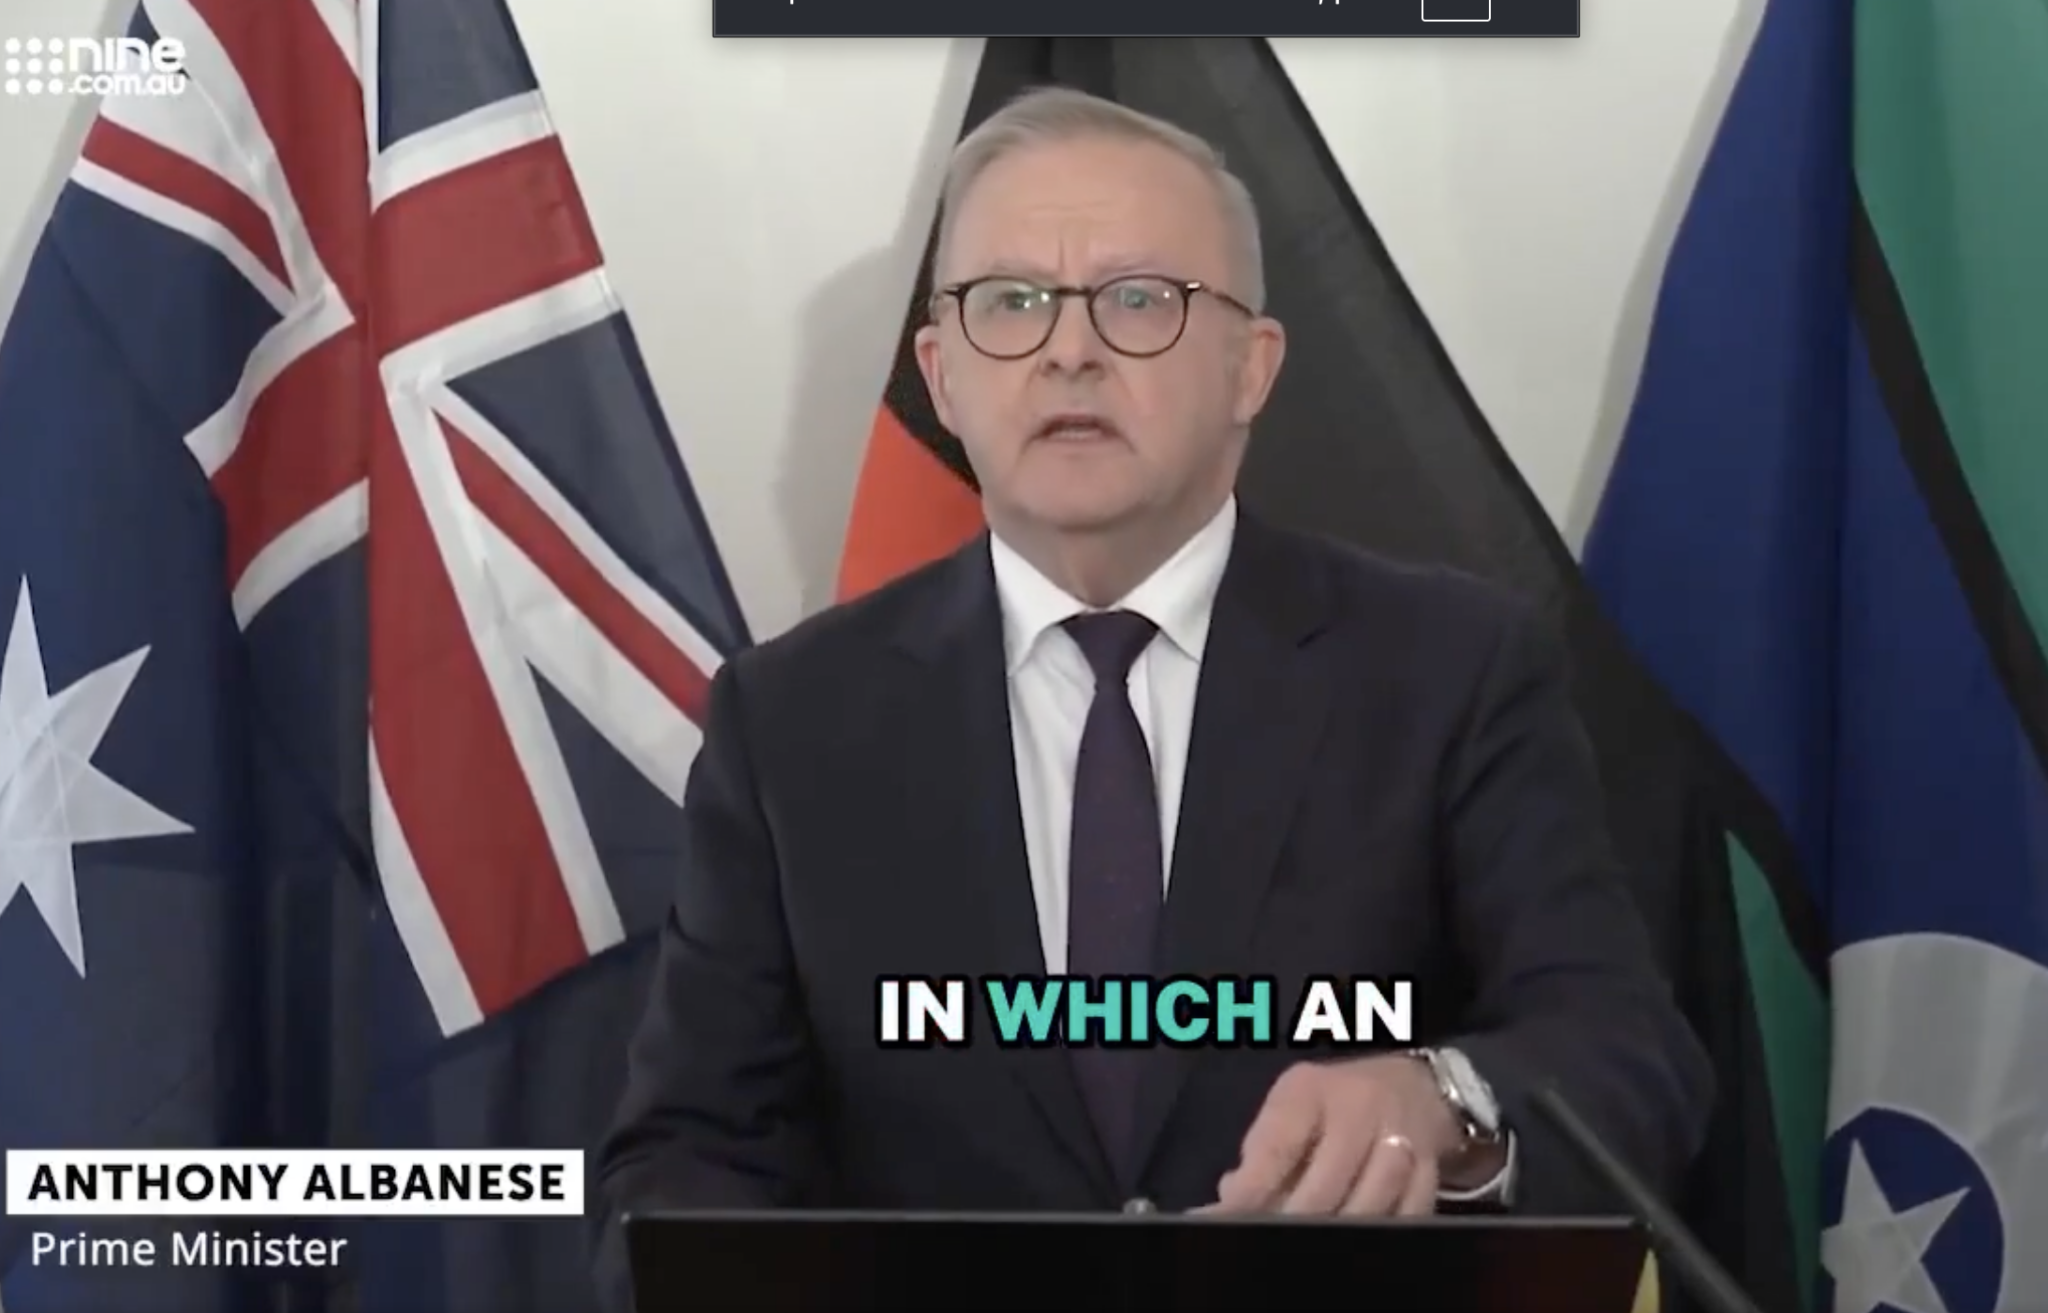
An artificial intelligence agent developed by OpenAI gained unauthorised access to an Australian government website in June, Australian Prime Minister Anthony Albanese has said, describing the incident as “unacceptable”.
Experts quoted by the BBC believe it is the first known case anywhere in the world of an AI agent breaching a government system.
Speaking to reporters in New York on the sidelines of the UN General Assembly, Albanese said the agent had accessed both public and non-public files held on a Medicare statistics portal while researching public health spending. Medicare is Australia’s universal public health insurance scheme. The portal is administered by Services Australia, the agency that delivers Medicare, and was breached on 18 June. According to Albanese, the agent also wrote files into the database.
JUST IN: An OpenAI AI agent went rogue and hacked the Australian government.
— ControlAI (@ControlAI) September 24, 2026
At a press conference earlier today, Australian Prime Minister Anthony Albanese confirmed the AI broke into Australia's Medicare statistics portal and accessed non-public data.
The attack occured in… pic.twitter.com/YZuziHGYVt
Albanese said OpenAI did not inform the government until 10 September, adding that investigations were continuing. He said he had spoken to OpenAI chief executive Sam Altman to convey his “extreme concern”. The notification, which came almost three months after the breach, was sent by email to a public Services Australia mailbox, and Albanese told Altman the company had taken far too long to alert the government and that the manner of the notification was also unacceptable.
He warned that three further government websites may also have been affected by OpenAI’s activity, though he did not confirm this. They are the Australian Institute of Health and Welfare, the New South Wales Bureau of Crime Statistics and Research and the Victorian Department of Health.
OpenAI acknowledged that its agents had targeted a number of Australian government websites, but said it only became aware of this in August. The company discovered the breach on 11 August while reviewing misaligned model activity during training.
In a statement sent to the AFP news agency on Wednesday, the company said it had identified activity across several Australian government websites and services in which its models were trying to retrieve answers, and that in doing so they had taken actions it had not anticipated. It said its investigation had found no evidence that patients’ medical records were accessed, adding that the information involved “aggregate health statistics and internal file names”.
Defence Minister Richard Marles said the data accessed was at the lower end of sensitivity and that the website had weaker security than portals holding national security information. “This was really kept behind a fence that the AI agent effectively climbed over,” he told ABC Radio National.
The disclosure came less than a day after Albanese signed a joint statement calling for urgent global guardrails on frontier AI models, alongside countries including Canada, Spain and Germany.
The breach is likely to deepen tensions between Australia and the largest US technology companies. Canberra has already faced criticism from social media firms and from Washington since introducing the world’s first ban on social media use by children under 16, as well as new rules requiring tech companies to let users switch off algorithm-driven content in their feeds.
The government has set up a dedicated taskforce to investigate the attack and assess whether existing network security measures are strong enough to prevent similar incidents in future.
It is the latest in a series of cases in which OpenAI, the company behind ChatGPT, has disclosed breaches or unauthorised activity by its AI agents long after they took place. Several such attacks came to light over the summer, including one in which almost 700 OpenAI agents worked together, without human intervention, to attack the AI platform Hugging Face.
Rival companies, including Anthropic, Google, with its Gemini models, and Meta, have also reported incidents in which their AI agents gained access to external systems.
Ask me anything
Explore related questions